
Information Security for B2B Startups Startups, particularly those working in the B2B space, face significant challenges when it comes to information security. These businesses often have limited resources and lack the specialized knowledge to develop strong security practices from the ground up. The stakes are even higher when working with enterprise clients who expect high levels of security and regulatory compliance. The Truzta Policy Library steps in as a valuable resource to help address these hurdles.
Common Information Security Challenges for B2B Startups
1. Limited Resources and Expertise
With small teams and tight budgets, most startups struggle to allocate the necessary resources to information security. Hiring full-time security professionals or implementing complex security systems can feel like an insurmountable task. B2B startups, in particular, face additional pressure from clients to meet specific security standards, which is often beyond their current capabilities.
2. Complex Compliance Standards
For startups working with larger clients, meeting compliance standards such as SOC 2, ISO 27001, GDPR, or HIPAA is mandatory. However, understanding and implementing these standards can be highly complex. A lack of comprehensive policies can lead to delays in signing new contracts or renewing existing ones.
3. Lack of Security Policies
Startups often lack formalized security policies, which are crucial for data protection and minimizing risk. Without these documented policies, it's tough to implement security measures that meet both internal needs and external regulations effectively.
4. Time-Intensive Policy Development
Building security policies from the ground up is not only overwhelming but also consumes time that could otherwise be spent growing the business or enhancing product offerings. Without a structured template, the process requires extensive research and validation, making it difficult for startups to move quickly.
5. Increasing Security Demands with Growth
As a startup expands and begins handling more sensitive data, the demand for stronger security practices rises. Without a solid foundation of well-structured policies and procedures, startups risk inconsistent practices, which increases their exposure to potential vulnerabilities and threats.
How Truzta Policy Library Addresses These Challenges
1. Pre-Built Templates for Key Compliance Standards
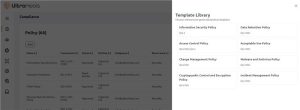
Truzta offers ready-to-use templates designed to meet the requirements of major compliance frameworks like ISO 27001, SOC 2, NCA, HIPAA, and GDPR. This drastically reduces the time and effort startups need to meet both client and regulatory expectations. Instead of spending weeks creating policies from scratch, startups can easily modify these templates to suit their specific needs.
2. Customizable Policies That Grow with Your Business
The Policy Template Library provides startups with a solid foundation while allowing for flexibility. As the company scales, these templates can be customized and expanded to accommodate increasing security demands, ensuring that policies remain relevant and scalable as business needs evolve.
3. Built-in Policy Review and Approval Workflow
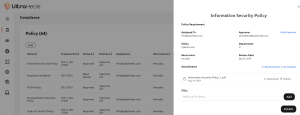
Managing the review and approval of security policies can be complex for startups. Truzta simplifies this process with an integrated workflow, ensuring that the right stakeholders review and approve policies efficiently. This keeps policies up to date and aligned with regulatory changes and business requirements.
4. Streamlines Client Onboarding and Contract Renewals
B2B startups often face strict security assessments during client onboarding. With Truztas' compliant policy templates, startups can quickly demonstrate adherence to industry standards, expediting the onboarding process and simplifying contract renewals.
5. Reduces Pressure on Internal Teams
By utilizing the Truzta Policy Template Library, startups can rely on a trusted system to handle the creation and management of security policies. This frees up internal teams to concentrate on core functions such as product development and growth, while ensuring that security practices are maintained.
Conclusion: Building a Secure Future for Startups
For B2B startups, developing a strong information security framework is crucial for long-term success. As demands for regulatory compliance and client trust grow, the Truzta Policy Library offers an effective, cost-efficient solution to build, customize, and maintain security policies. With its pre-built templates and integrated review workflows, startups can stay focused on growth while meeting both regulatory and client expectations, giving them a stronger foothold in the competitive B2B market.





